
Russia's Hybrid Cyber-Physical War in Europe Heats Up
A storm is raging in the form of cyber sabotage, disinformation, and drone attacks on European nations, particularly those that provide mate…
Appearance and language
Browse all headlines from this category in a dedicated page.
A storm is raging in the form of cyber sabotage, disinformation, and drone attacks on European nations, particularly those that provide mate…

This is an impressive piece of malware. Its sophistication says nation-state to me, but there is no direct evidence and certainly no attribu…

Agentic AI can smuggle arbitrary instructions from the Web, across multiple apps, into trusted internal communications channels.
New paper: “Self-Jailbreaking: Language Models Can Reason Themselves Out of Safety Alignment After Benign Reasoning Training.” Abstract: We …

The latest activity from the remote access Trojan (RAT) shows why organizations should monitor the behavior of applications rather than blin…
This is pretty amazing: However, the most astonishing thing about this break is that the GPT6 Astra did it entirely on its own. Carter Leff…
This installment of the Reporters' Notebook video series discusses the impact of AI agents breaching Hugging Face, Fairlife's ransomware att…
Keeping edge computing safe requires organizations to fundamentally rethink security governance. Here is a path forward: a step-by-step guid…
Even if the organization locks down employee accounts, forgotten and lost service accounts can still undo the organization's entire M365 env…
AI apps that interpret external data (read: most AI apps) need exceptionally rigorous security filters, or attackers can take advantage.
Enterprise computing is moving to the edge. Keeping it secure requires tactics far beyond putting up firewalls.
A process parameter-poisoning technique evades EDR by injecting code into process initialization structures without using the Windows APIs t…
Incoming email addresses automatically assigned to each user on the platform contain highly privileged access tokens that attackers can use.
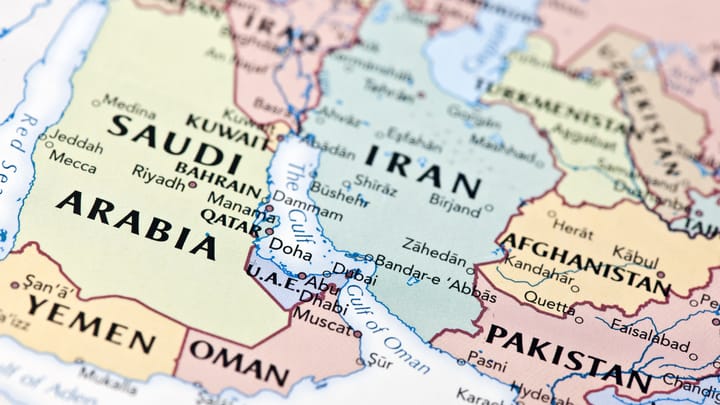
The United Arab Emirates and Kingdom of Saudi Arabia together absorbed 50% of all cyberattacks recorded across the Gulf region in the first …
Threat actors are poisoning ChatGPT, Gemini, and Google AI Overview answers by seeding the Web with malicious links and data and then optimi…
More than 80,000 AI relay servers are helping users in China mask their identities while they access cutting-edge large language models (LLM…
Cybersecurity and brand reputation are inextricably linked. Security and marketing leaders who establish regular touchpoints, develop joint …
Microsoft seized 50 websites and disabled more than 150 domains as part of a coordinated disruption effort against a phishing-as-a-service p…
The Cybersecurity and Infrastructure Security Agency (CISA) is going old school to help organizations with limited resources set traps for h…
As more reports of misalignment incidents underscore AI risks, large AI labs, regular businesses, and even nations are searching for better …
Industrial companies are increasing cybersecurity investment as connected operations, AI adoption, and IT/OT convergence expand operational …
Threat actors stole the contents of 170 private repositories using an OAuth token stolen from a former employee's computer through the TanSt…

Unbounded consumption is an issue that OWASP currently ranks sixth in its Top 10 for LLM Applications, and it could be an extremely costly o…
ShinyHunters defaced Cl0p's Dark Web site and claims to have stolen victim data, potentially exposing organizations that paid ransoms to ren…